Sometimes the antidote for something that initially creates hysteria is doing nothing more than waiting until all of the facts are known. It is one of the reasons why first-hand accounts of “breaking news” in many cases turn out to be less than reliable. This week saw a terrific example of this as a result of a headline from ZDNet that read, “Bigger than Heartbleed, 'Venom' security vulnerability threatens most datacenters.”
I will admit it not only got my attention but filled up my inbox with all kinds of speculation and advice. After all, if the headline portraying the degree to which the VENOM (Virtualized Environment Neglected Operations Manipulation) vulnerability could cause havoc globally in a data center-centric world was even close to a rough approximation, how far behind would be true Armageddon? As the week progressed, the good news is that VENOM could inflict pain but it is safe to say getting bitten and injected is problematic at best, and there already is a fix.
Knowledge is power
So at the close of the week, here is what we know and why peace of mind is obtainable when it comes to this potentially very bad, poisonous boy.
First, the zero-day flaw takes advantage of the “virtual floppy disk controller.” That is serious since it would enable attackers to escape out of the virtual machine and execute malicious code on its host. However, security experts now seem to unanimously agree that to take advantage of the
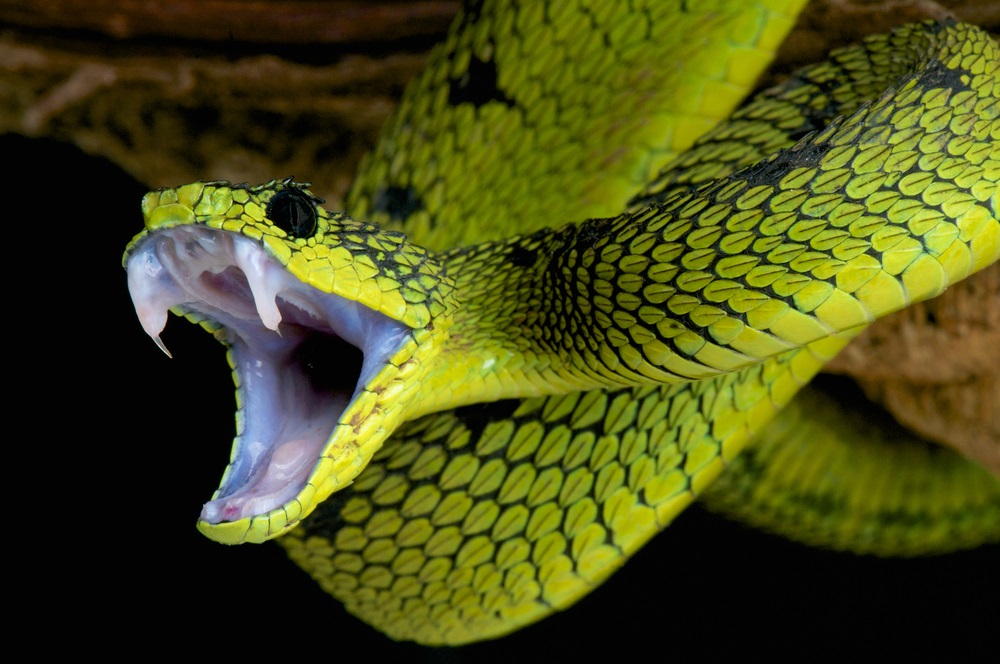 Image via Shutterstock
flaw a hacker would have to gain access to a virtual machine with high or ‘root’ privileges of the system. Plus, they could not do this remotely which (pardon the pun) is a major barrier to entry.
Second, the original estimate of the number of data centers that could be compromised was several orders of magnitude too high. Realities are that virtualization products that could be affected include XEN, KVM, QEMU and VirtualBox. Noticeable by their absence on this list are VMware and Microsoft, and thus far AWS Xen instances are not affected by the VENOM VM escape bug. Hence, it appears that the not susceptible list represents a huge slug for the entire potentially vulnerable market.
Third, there is no indication that this vulnerability has gone wild.
Finally, fixes are available to remediate the possibility of being poisoned although customers of hosted virtual server service providers are being encouraged to check that their vendor is protected.
This is not to minimize or trivialize by any means the threat ultimately posed by virtualized system-to-host vulnerabilities. Just because VENOM may have gotten people a bit over anxious in fact may not have been a bad thing. As Gavin Reid, VP of threat intelligence, Lancope commented, “Mass compromise of hosting infrastructures (such as seen in darkleach) are an integral part of creating the underground economies backbone infrastructure and ability to scale. Miscreants will be turning attention to weaponizing this and once that is done - for the bad guys, a mass-hack of a virtualized environment could be one rented server away.”
Warming to the sub-head above about knowledge being power, Reid’s colleague TK Keanini, CTO, Lancope added: “Moving to the cloud means having visibility in the cloud. This is not the first vulnerability to be exposed like it nor will it be the last so the questions becomes, when will you find out about it: before, during, or after? While you will never be perfect, the earlier you can gain visibility on the attack the better.”
Ken Westin, Security Analyst from Tripwire agrees, “High impact vulnerabilities such as Heartbleed and Shellshock are going to be the new normal and they can appear anywhere in your software/hardware stack. The most important thing organizations can do to get a head of these is to take an inventory of their hardware and software assets and be able to quickly identify what systems are vulnerable and remediate them as fast as possible, hopefully before exploits are released into the wild.”
It appears as the weekend approaches that IT professionals can all take a deep breath on this one and hopefully catch up on their sleep.
Edited by
Maurice Nagle